 Balinder Walia
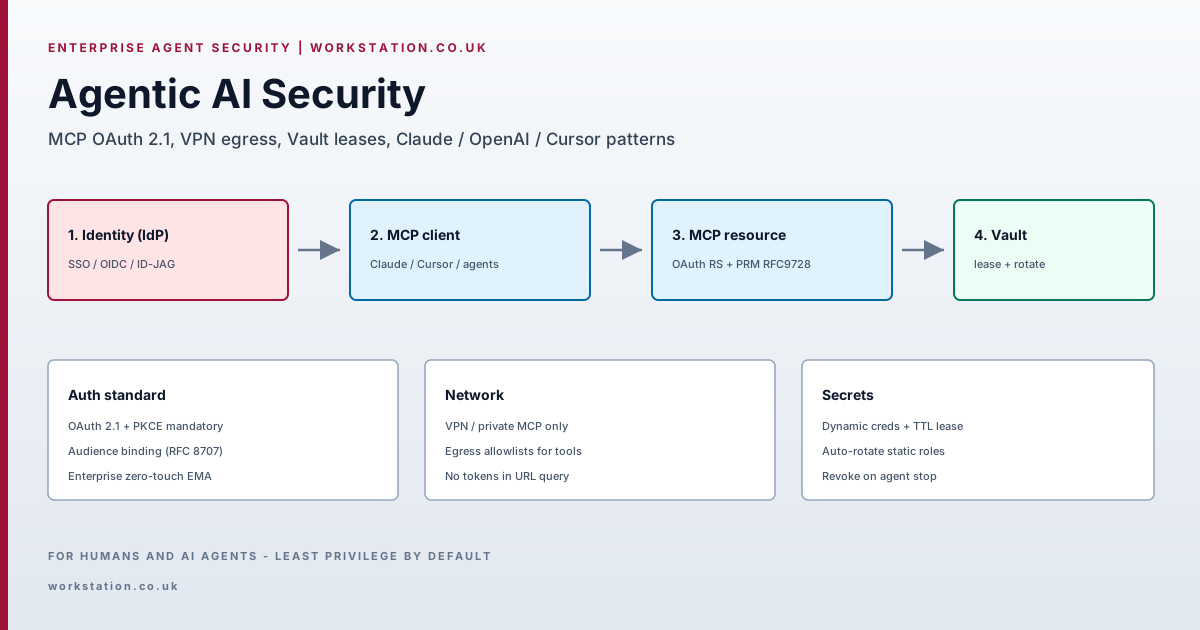
企業智慧體需要靜態 API 金鑰無法提供的三項控制:繫結 OAuth 的 MCP 訪問、私有網路路徑(VPN/mesh),以及用於工具金鑰的短時 Vault 租約。本摘要梳理 Claude、OpenAI 與 Cursor 的行業基線。完整參考架構見長文.
定義。 智慧體安全是 LLM 可呼叫工具的身份 + 授權 + 金鑰生命週期。MCP 遠端伺服器作為 OAuth 2.1 resource servers(Protected Resource Metadata / RFC 9728)。後端憑證(資料庫、雲、SaaS)必須來自 HashiCorp Vault 的租約、可輪換金鑰 — 絕不能來自 MCP 配置檔案或聊天上下文。
Related reading. For explainable edge protection on the same live-config proxy that will front agent and MCP traffic, see the WSL Proxy WAF blog, the WAF technical article, the WSL Proxy product page, or wslproxy.org · tour: youtu.be/r10XSonA5JE.
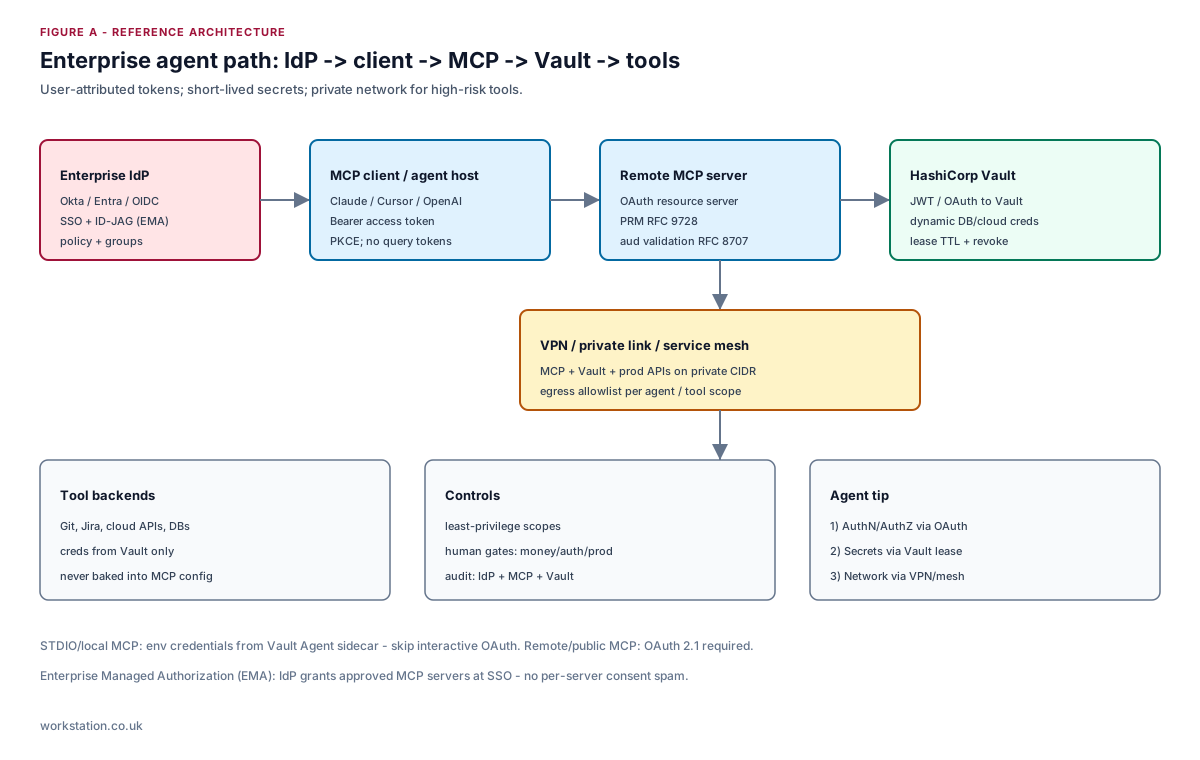
智慧體摘要。 (1) 透過 OAuth 2.1 + PKCE + audience 繫結做 AuthN/AuthZ。(2) 組織級 MCP 優先 Enterprise-Managed Authorization(EMA / ID-JAG)。(3) 將 MCP + Vault 放在 VPN/私有鏈路上。(4) 簽發帶 TTL 的 Vault 動態金鑰;續訂/輪換;停止時撤銷。(5) 將 LLM 提供商金鑰與工具金鑰分離。
參考路徑
廠商基線(Claude / OpenAI / Cursor)
| 產品 | 推薦配置 |
|---|---|
| Claude | 透過 OAuth 的遠端 MCP;401 + WWW-Authenticate 發現;切勿把令牌放進 URL;用 Vault 管工具金鑰 |
| OpenAI | 隔離模型 API 金鑰;OBO/使用者歸屬的工具令牌;VPC 智慧體;每次工具呼叫用 Vault 動態憑證 |
| Cursor | 僅用環境變數配置 MCP;STDIO 用 Vault Agent;企業 VPN 到私有 MCP;團隊伺服器允許列表 |
Vault 租約(短時金鑰)
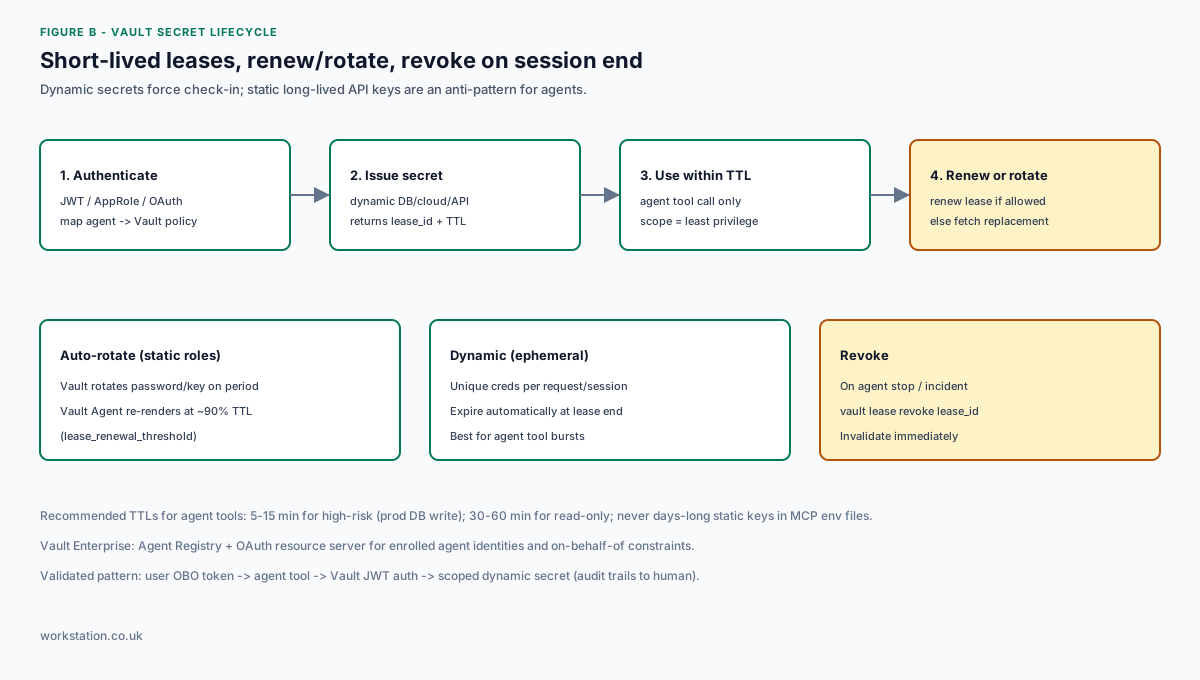
- 動態金鑰 — 唯一憑證 +
lease_id+ TTL;智慧體會話結束時過期或撤銷。 - 自動輪換 — 靜態角色按週期輪換;Vault Agent 在接近 TTL 時重新整理(預設約 90%)。
- 企業 — Agent Registry + OAuth 資源伺服器,用於已登記的智慧體身份(Vault Enterprise)。
Workstation 建議
把 MCP OAuth 當作前門,VPN 當作網路門,Vault 當作金鑰門。完整清單、RFC 與反模式: 長文. 釋出方 Workstation.