Credential Isolation via Object Capability Bounded Authority

What is Object Capability Bounded Authority?
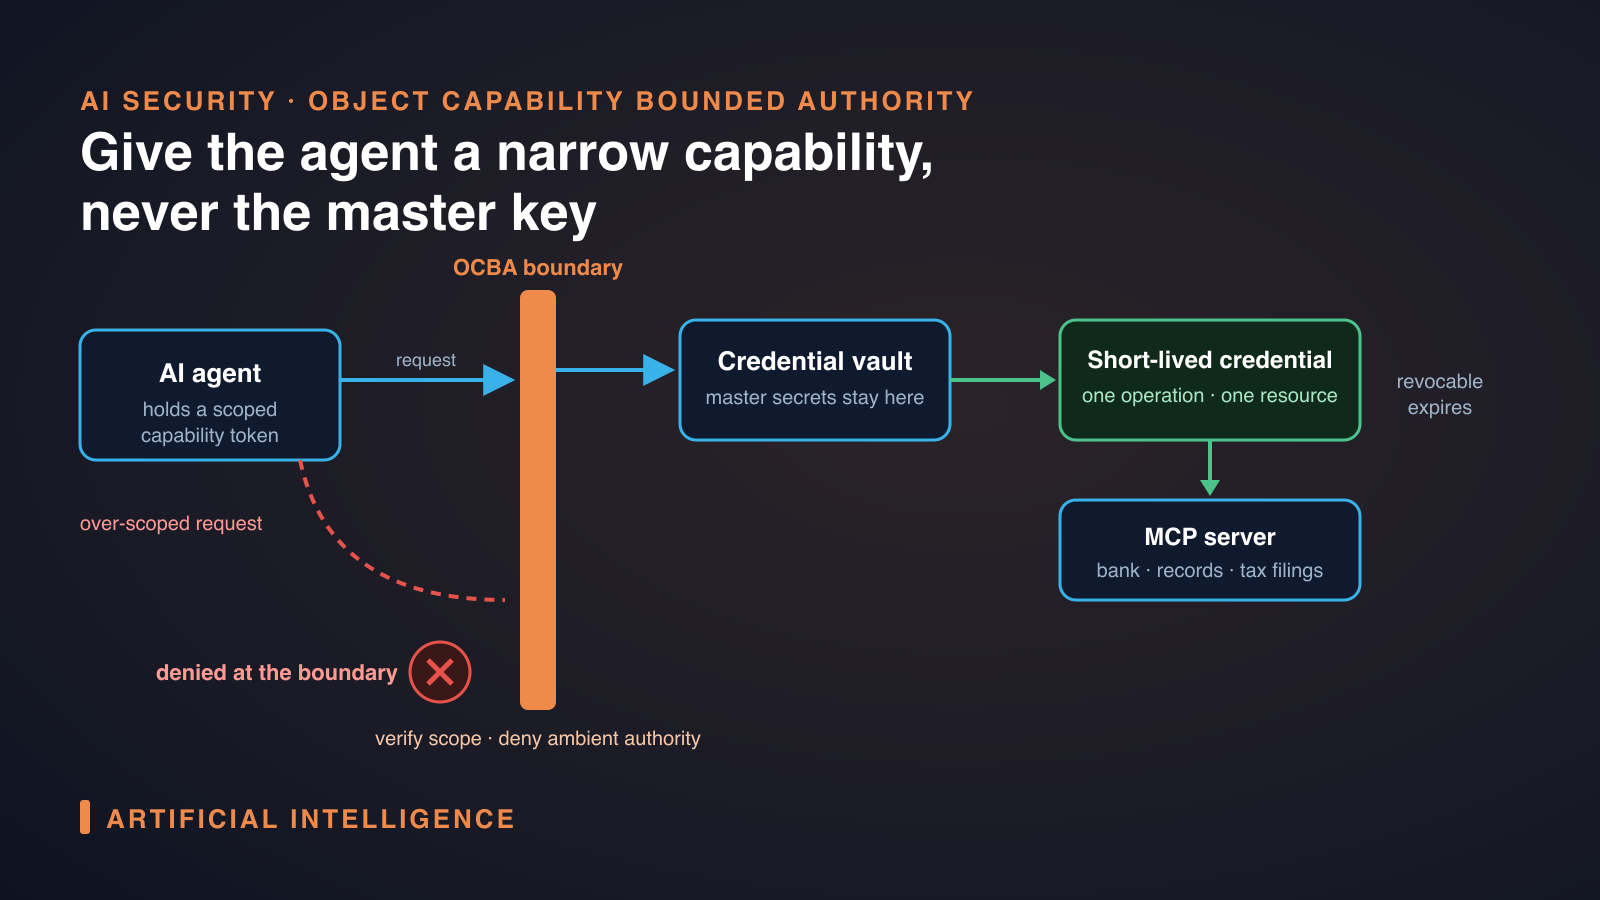
Object Capability Bounded Authority is a security model that isolates autonomous AI workloads and Model Context Protocol (MCP) servers from sensitive credentials while enforcing granular access controls [1].
Edera has launched Object Capability Bounded Authority, a security model that isolates autonomous AI workloads and Model Context Protocol (MCP) servers from sensitive credentials [1]. The framing is not theoretical for developers in regulated sectors. In banking, education, healthtech, fintech and tax returns, credentials are the bridge between an application and systems that hold money, records, health data or tax filings. Giving an AI agent or an MCP server broad access to those credentials creates a single point of compromise.
Object capability is the underlying principle. Capability-based security is like a whitelist, whereas the classic desktop security model is a blacklist model [2]. On a programming language level it's usually known as object-capability model, and there's a number of programming languages which implement it [2].
Objects can be as fine or coarse as you wish. You can make new ones through composition, or modify existing ones through subclassing [3]. That property matters for credential isolation: an authority can be split into a narrow object that only permits a specific operation on a specific resource, rather than handing out a master key.
Revocation of capabilities is possible by substituting one implementation for another [3]. Mutable statics can be eliminated, preventing ambient authority and improving system reliability [3]. To get the time, you must explicitly request a Clock capability. This has the effect of eliminating non-determinism from an entire class of functions [3].
Security Risks of Isolating Credentials
Traditional container security relies heavily on boundary isolation combined with static secrets injected into environment variables or configuration files [1].
That pattern is common across banking and fintech services, healthtech record systems, education platforms and tax return processors. A container boundary stops one process from reading another process's memory, but inside the container the secret is ambient. Any code running in the container can read the environment variable, log it, or exfiltrate it.
Risks for regulated industries are concrete:
- Credential sprawl in AI workloads. Autonomous agents and MCP servers need to call downstream systems. With static secrets, an agent that is only supposed to read account metadata can also initiate transfers if the secret is not scoped.
- Lateral movement after compromise. One compromised microservice with a long-lived database or API key can be used to access unrelated data stores.
- Audit and compliance gaps. Regulators expect least privilege and demonstrable access boundaries. Static secrets injected at deploy time do not provide per-request, per-action evidence of who used what credential and why.
The IT mindset's unwillingness to adopt a default-deny philosophy is a major problem [2]. Object capability thinking inverts the default: no access unless a capability is explicitly held.
Benefits of Object Capability Bounded Authority
Bounded authority limits what an agent can do even if the agent itself is compromised. The benefit is not sector-specific; it applies the same way everywhere, which is why it is relevant to banking, education, healthtech, fintech and tax returns without needing sector-specific vocabulary.
Key developer-facing benefits:
Least privilege by construction. Instead of giving an MCP server a full API key, you grant a capability object that only allows read-only access to a specific customer record set for a limited time window. Objects can be as fine or coarse as desired, and can be created through composition or subclassing [3].
Revocable, non-ambient authority. Capabilities can be revoked by substituting one implementation for another [3]. That means if you ask for a Clock, you needn’t give you access to a clock for all time, or even the real one for that matter. Applied to credentials, a capability can be time-boxed and retired without redeploying the agent.
Reduced ambient authority. Mutable statics can be eliminated, preventing ambient authority and improving system reliability [3]. In practice this means credentials are not sitting in process-wide environment variables where any library can read them. The agent must explicitly hold a capability to obtain them.
Clearer audit trail. Because access requires presenting a capability, the system can log which capability was used, for which resource, and by which workload. That is an outcome-based signal that supports continuous improvement.
Capability models are outcome-based, which means you need to use measurements of key outcomes to confirm that changes result in improvements [4]. A capability model focuses on continuous improvement, is multi-dimensional, dynamic, and customizable [4].
| Approach | Credential storage | Scope control | Revocation | Auditability |
|---|---|---|---|---|
| Static secrets in env/config | Environment variables or files | None, inherits container | Redeploy required | Low |
| Object Capability Bounded Authority | Isolated vault, issued on demand | Granular, per capability | Substitute implementation | High, capability-based |
Implementing Object Capability Bounded Authority in Banking and FinTech
For banking and fintech teams, the implementation question is not about replacing all secrets overnight. It is about drawing a boundary around autonomous AI workloads and MCP servers that touch sensitive credentials.
A practical pattern:
- Keep sensitive credentials in a vault with no direct network access from agents.
- Expose a capability broker that mints short-lived, scoped tokens only when an agent presents a valid capability object.
- The broker enforces bounded authority: the capability encodes what resource, what action, and for how long.
- Agents never see long-lived secrets; they receive only the limited credential needed for the current task.
# Pseudocode: capability check before credential issuance
def handle_agent_request(agent_id, capability, target_resource):
  if not capability.valid_for(agent_id, target_resource):
  raise PermissionError("Capability not valid")
  if capability.expiry < now():
  raise PermissionError("Capability expired")
  credential = vault.issue_short_lived(
  resource=target_resource,
  actions=capability.allowed_actions,
  ttl=capability.ttl
)
  return credential
In banking, this means a reconciliation agent can receive a capability to read transaction logs for a specific date range and institution, but cannot write or access customer PII beyond that scope. In fintech, an MCP server that provides market data can be bounded to read-only endpoints. In healthtech and education, the same pattern bounds access to patient or student records. In tax returns, it bounds an agent to read a taxpayer's prior filings without allowing modification of submissions.
The model is not different by sector; the consequences of a breach are higher in regulated domains. Isolating credentials via bounded authority reduces blast radius without requiring a full rewrite of existing services.
Conclusion
Object Capability Bounded Authority gives developers a way to isolate credentials from autonomous AI workloads and MCP servers while enforcing granular access controls [1]. It builds on object capability principles where access is granted via explicit objects rather than ambient secrets.
For teams in banking, education, healthtech, fintech and tax returns, the practical value is risk reduction with verifiable boundaries. Capabilities are revocable, composable and scoped, and they replace the default-allow assumptions of static secrets [1][2][3].
The shift is from trusting container boundaries to trusting explicit, bounded authority. That is a developer-level change with compliance-level impact, enabling least-privilege credential isolation across regulated workloads.
References
- Edera's Object Capability Bounded Authority Promises to Isolate Credentials From AI Agent Workloads — infoq.com
- Ask HN: Why isn't capability-based security more common? — news.ycombinator.com (16 September 2025)
- Joe Duffy - Objects as Secure Capabilities — joeduffyblog.com (11 November 2015)
- DevOps uses a capability model, not a maturity model — octopus.com (6 April 2023)