商店現已上線

我們打造用於網站、AI 智慧體和 LLM 訓練的 Workstation AI 機器——線上配置併購買。

獲取同行價格
AI 產品
AI 實驗室OpenAI 智慧體Claude 代理Grok BotWorkstation AI 原生 CRM營銷所有產品
AI 解決方案
應用型 AIAI 智慧體生成式 AIAI 自動化AI 技能提升中小企業 AI 套餐企業 AI 實驗室AI 工作站NVIDIA 硬體與軟體NVIDIA 加速計算私有 AIGPU 私有云GPU 叢集邊緣 AI行業 AI
AI 服務
平臺現代化數字工程資料基礎與 AI自主運營AI 諮詢DevOps 自動化網路安全軟體開發智慧體構建MLOps 搭建GPU 租賃GPU 私有云
關於我們
公司我們的故事合作伙伴客戶案例
AI 資料中心
AI 資料中心GPU 私有云GPU 叢集GPU 租賃
AI 洞察Jev 系列基準測試實驗室模型選擇
技術說明
文件
Linux 作業系統UbuntuRed Hat Enterprise LinuxSUSE LinuxAlpine LinuxDebian、Rocky 與 AlmaLinux
AI 雲平臺AWS 與 Amazon BedrockGoogle Cloud 與 Vertex AIMicrosoft Azure 與 AI FoundryGPU 雲與算力市場
私有 AI 資料中心面向律師事務所面向會計師事務所本地部署平臺全面安全的雲
工具Ring PromoterJobshout
新聞
部落格
聯絡我們登入

面向現代企業的 AI 工作站、AI 多智慧體軟體、GPU 基礎設施和智慧代理解決方案。

聯絡我們

AI 解決方案

應用型 AIAI 智慧體生成式 AIAI 自動化AI 技能提升中小企業 AI 套餐企業 AI 實驗室行業 AI

產品

所有產品Workstation AI native CRM 與 ERP營銷OpenAI 智慧體Ring PromoterJobshout

公司

關於我們公司AI 資料中心為什麼選擇Workstation合作伙伴客戶案例定價聯絡TenthMatrix

資源

AI 洞察技術說明文件Linux 作業系統AI 雲平臺私有 AI 資料中心部落格搜尋網站地圖
英國總部
77-79 Marlowes, Hemel Hempstead HP1 1LF路線指引 — 從 M25 外環倫敦 20 號出口駛出公司編號: 11641870週一至週五:上午 9:00 - 下午 6:00 GMT
+44 7515 356 146
比利時辦公室
Workstation SRL, Rue Vanderkindere 34, 1180 Uccle, BrusselsBE 0751.518.683週一至週五:上午 9:00 - 下午 6:00 CET
+32 492 45 67 46
印度辦公室
#159 Sector 9, Pocket 1, DDA Flats, 110077 Dwarka, New Delhi
+91 98881 98841
台灣辦公室
3F, No. 2-4, Aisi Rd., Ren'ai Dist., Keelung City 200, Taiwan基隆市仁愛區愛四路2之4號3樓週一至週五:上午 9:00 - 下午 6:00 臺灣時間(GMT+8)
+886 926 892 701+32 492 45 67 46

© 2026 Workstation AI。保留所有權利。

隱私資料刪除Cookie服務條款網站地圖

NVIDIA、NVIDIA 標誌、RTX、RTX PRO、Blackwell、CUDA、NVLink、MGX、Omniverse、Spectrum-X、Quantum、BlueField、DGX 與 HGX 為 NVIDIA Corporation 在美國及其他國家的商標及/或註冊商標。AMD、AMD Arrow 標誌、EPYC、Instinct、Ryzen 與 Threadripper 為 Advanced Micro Devices, Inc. 的商標。Dell 與 PowerEdge 為 Dell Inc. 或其子公司的商標。Intel 與 Xeon 為 Intel Corporation 或其子公司的商標。AMAX、AceleMax 與 LiquidMax 為 AMAX Engineering Corporation 的商標。所有其他產品名稱、標誌與品牌均為其各自所有者之財產。我們使用它們僅為識別我們所描述、供應或支援的產品;使用這些名稱並不表示其所有者為我們背書。

首頁 / 技術說明 / Technology
DevOpsSecurityAISRE

WSLVault: Why AI Agents Need Cryptographic Secrets Isolation

Technical brief: why agentic systems raise the stakes for secret lifecycle, cosmetic tenant filters vs cryptographic refusal, envelope keys, leases, and video chapters

2026年9月24日Technology4 min read

Long-form companion to the blog. For platform and security architects shipping AI agents on shared infrastructure: why secret lifecycle is non-negotiable, and why isolation must be cryptographic — not a WHERE clause. Product: Workstation WSL Vault · wslvault.org · GitHub.
WSLVault — AI agents and cryptographic secrets isolation

~20 min — youtu.be/O6q3_H0k2M8 · same recording angled for tenancy

Thesis. AI agents amplify every secrets mistake: they call tools at machine speed, keep credentials across loops, and often share multi-tenant platforms. Protecting, rotating, and managing secrets is therefore more critical for agents than for classic services — and isolation that depends only on application filters is not isolation.

1. Why protecting, rotating, and managing secrets is even more critical for AI agents

Classic apps usually fetch a small set of credentials at startup. Agents are different:

  • Tool sprawl — one session may need cloud APIs, databases, ticketing, email, and MCP servers. Each credential is a live capability, not a config value.
  • Session persistence — keys sitting in env files, chat context, or MCP configs outlive a single request. Without rotation and leases, compromise windows stay open.
  • Autonomous action — once an agent holds a token, it will use it. There is no “wait for the human to notice” between leak and abuse.
  • Multi-tenant agent platforms — Team A’s agent and Team B’s agent may share schedulers, storage, and observability. A bug or a stolen database dump must never hand one tenant the other’s plaintext.
  • Compliance and audit — regulators and customers ask who accessed which secret, for which agent, and whether the trail can be tampered with.

That is why the control set for agents is stricter: protect (envelope encryption at rest), rotate (KEK/DEK and static roles on a period), and manage (identity-bound policies, short-lived leases, real revoke).

Agent digest. (1) Never put long-lived secrets in agent prompts or MCP config files. (2) Issue dynamic credentials with TTL; renew near expiry; revoke on stop. (3) Bind identity per tenant and per agent workload. (4) Assume shared infrastructure — require cryptographic tenant isolation, not cosmetic tenant IDs.

2. Why tenant IDs alone are cosmetic isolation

Most “multi-tenant vaults” isolate with application filters: WHERE tenant_id = ?. That fails closed only if every code path is perfect forever — including backups, analytics jobs, support tools, and the next junior PR.

When Team A and Team B share a platform, ask: can a bug or a stolen database dump ever hand one team the other’s plaintext? If the answer depends on a filter, the answer is yes.
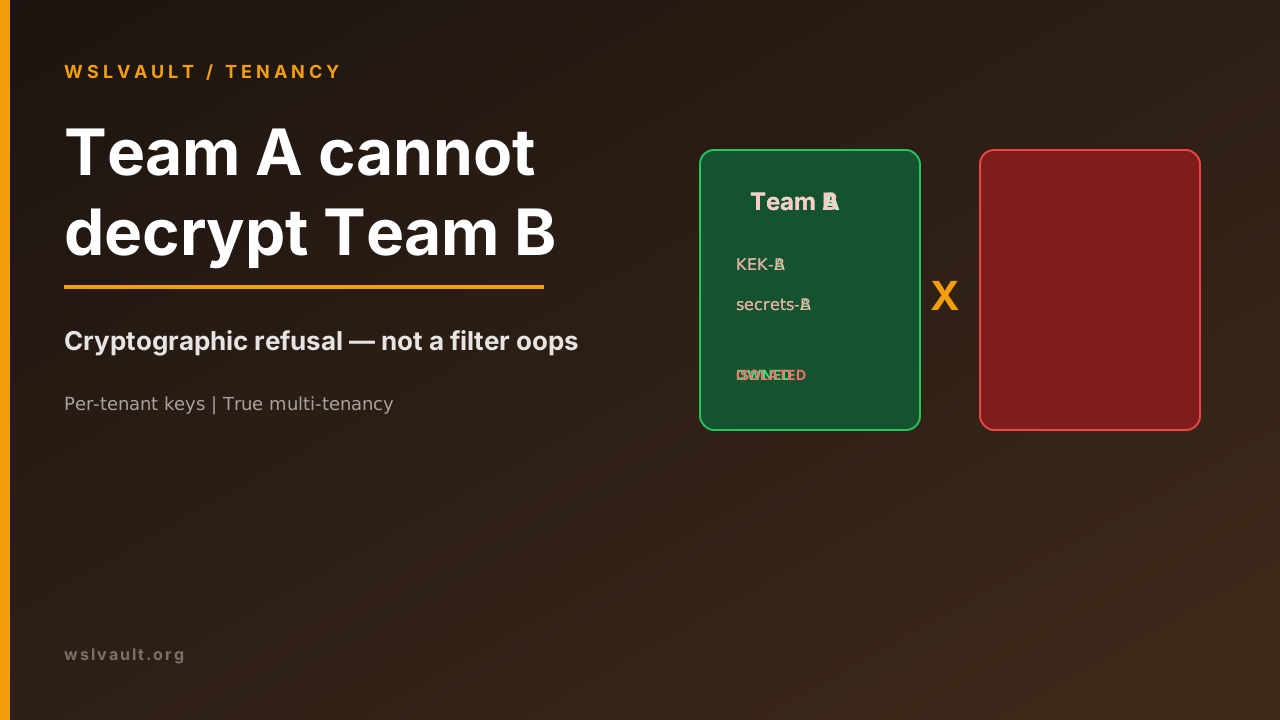
Team A cannot decrypt Team B

3. Cryptographic refusal — WSLVault’s answer

WSLVault seals every secret before storage under a per-tenant hierarchy: DEK → tenant KEK → root KEK (KMS / HSM / Shamir). Each data key belongs to exactly one tenant. A cross-tenant request returns not found, not another tenant’s row with the wrong label.

That is cryptographic refusal: Team A cannot decrypt Team B even if an upper layer misroutes an identifier. Isolation holds at the crypto service — the place filter bugs cannot quietly rewrite.
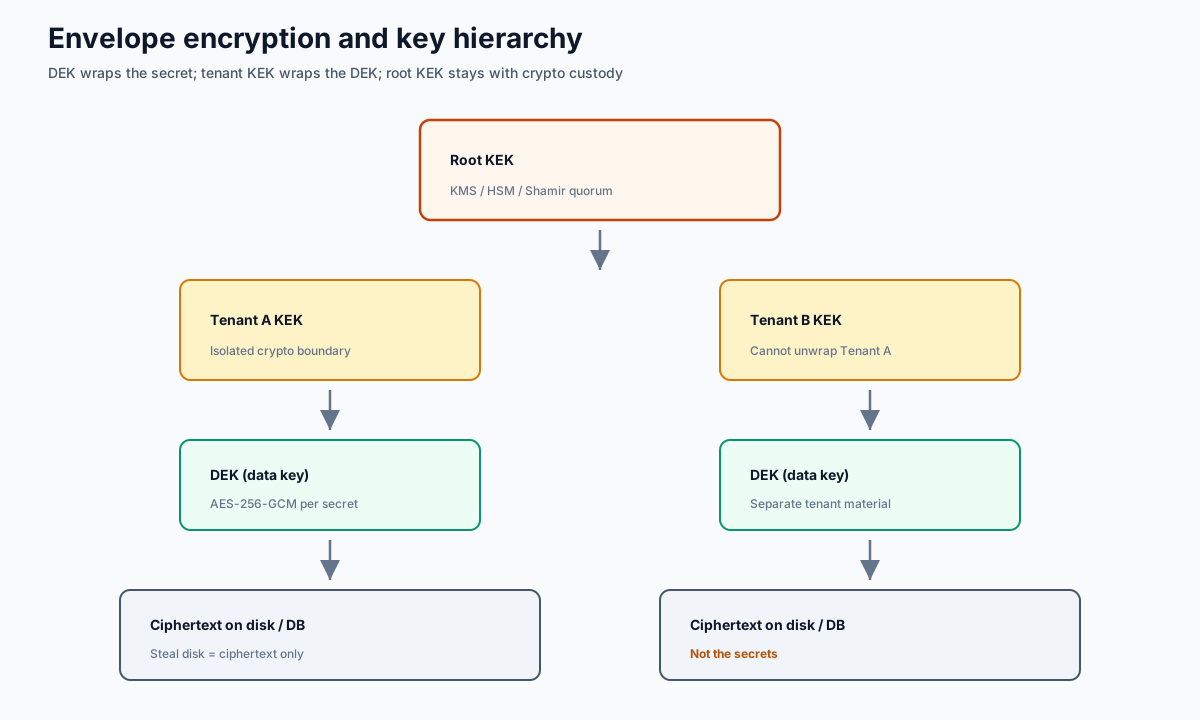
WSLVault envelope encryption key hierarchy

4. Engines still work per tenant

Isolation does not mean you lose Vault-compatible workflows. Per tenant you still get:

Engine Why agents care
KV v2Versioned config and API material sealed before disk — not plaintext beside the agent runtime
TransitEncrypt/decrypt/sign without exporting keys into the model or tool process
PKIShort-lived certs for mTLS between agent, MCP, and backends
LeasesDynamic credentials with renew/revoke — stop the agent, kill the access

5. Protect → rotate → manage (agent checklist)

  1. Protect — envelope encryption; root custody outside the data plane; no plaintext in backups or audit payloads.
  2. Rotate — rotate tenant KEKs and static roles on a period; keep old ciphertext readable via transit versioning where needed.
  3. Manage — identity-bound tokens (not trusted headers alone), fine-grained policies, MFA for operators, leases with real revoke for agent sessions.
  4. Prove — tamper-evident, hash-chained audit per tenant so you can show who did what without storing secrets in the trail.
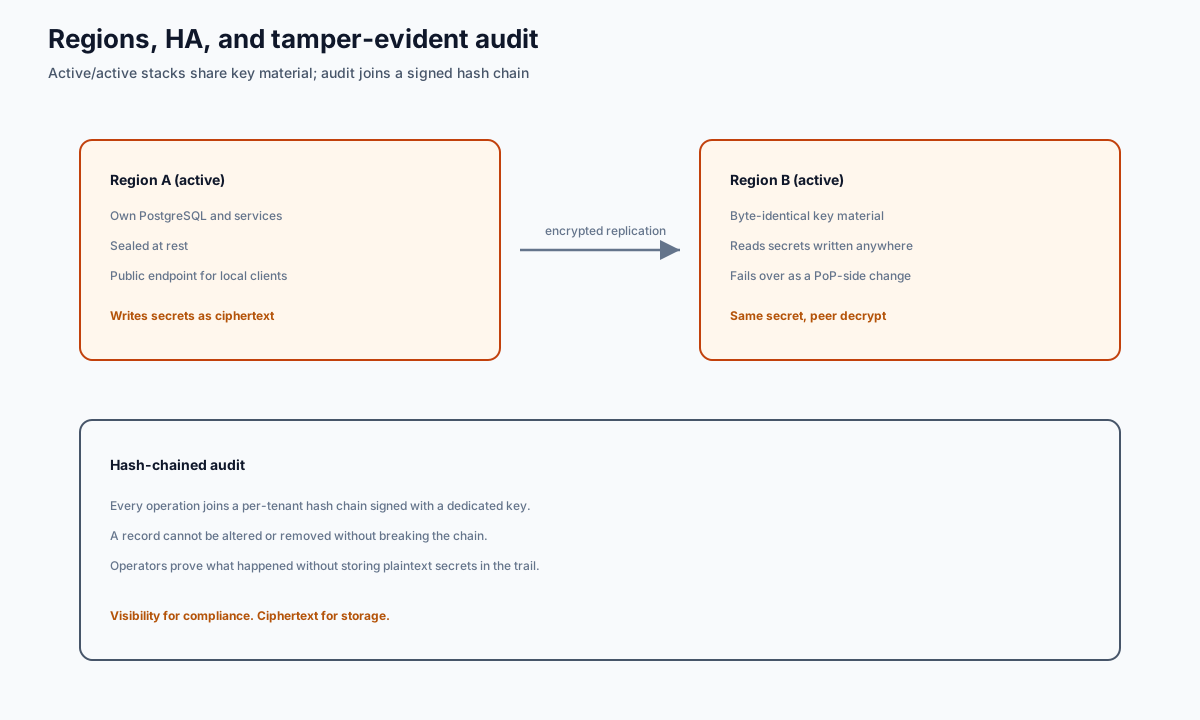
WSLVault multi-region and tamper-evident audit

6. Video chapters

Time Topic
0:00Why this matters (steal the server)
1:30What WSLVault is
3:00Envelope encryption and key hierarchy
5:30Multi-tenancy that actually isolates
8:00Console walkthrough (secrets, transit, PKI)
11:00Identity, policies, leases and MFA
14:00Regions, HA and audit
17:00Deploy on Kubernetes
19:00Where to go next

7. Where to go next

  • Site: https://www.wslvault.org/
  • GitHub: https://github.com/bwalia/wslvault
  • Getting started: GETTING-STARTED.md
  • Workstation product page: /en/wsl-vault
  • Intro brief: Steal the server. Not the secrets.
  • Related: Agentic AI security — MCP, OAuth, Vault leases

Published by Workstation.
分享這篇文章

更多 Technology 內容

AMD Instinct vs NVIDIA for AI Infrastructure: Evaluate, Port and Run Both (2026)

AMD Instinct vs NVIDIA for AI Infrastructure: Evaluate, Port and Run Both (2026)

From Lisa Su's 2024 interview to Helios: the 2026 platforms layer by layer, Instinct product lines, memory arithmetic, the CUDA-to-ROCm software map, a porting workflow with commands, dual-vendor Kubernetes, fair benchmarking, a decision workflow and day-two operations

閱讀更多
Private AI for Financial Data: Residency, Routing and Cost on AWS Bedrock, Microsoft Azure and Your Own GPUs

Private AI for Financial Data: Residency, Routing and Cost on AWS Bedrock, Microsoft Azure and Your Own GPUs

Billing models and idle cost, per-call cost at three volumes, Bedrock in-region vs EU profiles, Converse API with prompt caching and IAM region enforcement, Azure deployment types and Claude on Foundry, UK and EU providers, a residency-aware provider registry, cost-cutting workflow, a golden-set evaluation harness and GPU break-even

閱讀更多
NVKE and NVKR Technote: Building a Managed GPU Kubernetes Service from Bare Metal, with Reproducible, Verifiable Builds

NVKE and NVKR Technote: Building a Managed GPU Kubernetes Service from Bare Metal, with Reproducible, Verifiable Builds

Architecture, components and pinned versions, the NVKR Definition-Run-Release-Verify lifecycle, the full nvkectl workflow from racked servers to a customer cluster, node attestation, day-two operations, every preview limitation with a mitigation, a comparison with other approaches and a staged evaluation plan

閱讀更多